Find out what an attacker would find... before they do.
The OXEN Advantage
What’s Included
OXEN Penetration Testing combines automated assessment, expert manual testing, risk analysis, and strategic reporting within one coordinated engagement. These capabilities help organizations move beyond assumptions and understand how weaknesses could be used to compromise systems, disrupt operations, or expose sensitive information.
Simulates the tactics and techniques used by cybercriminals to evaluate the effectiveness of existing security controls.
Confirms which vulnerabilities are truly exploitable, helping organizations focus on risks that matter most.
Assesses both internet-facing and internal systems to provide a comprehensive view of security exposure.
Prioritizes identified vulnerabilities based on potential business impact, likelihood of exploitation, and overall risk.
Delivers clear recommendations to help IT and security teams efficiently address identified weaknesses.

Business Outcomes
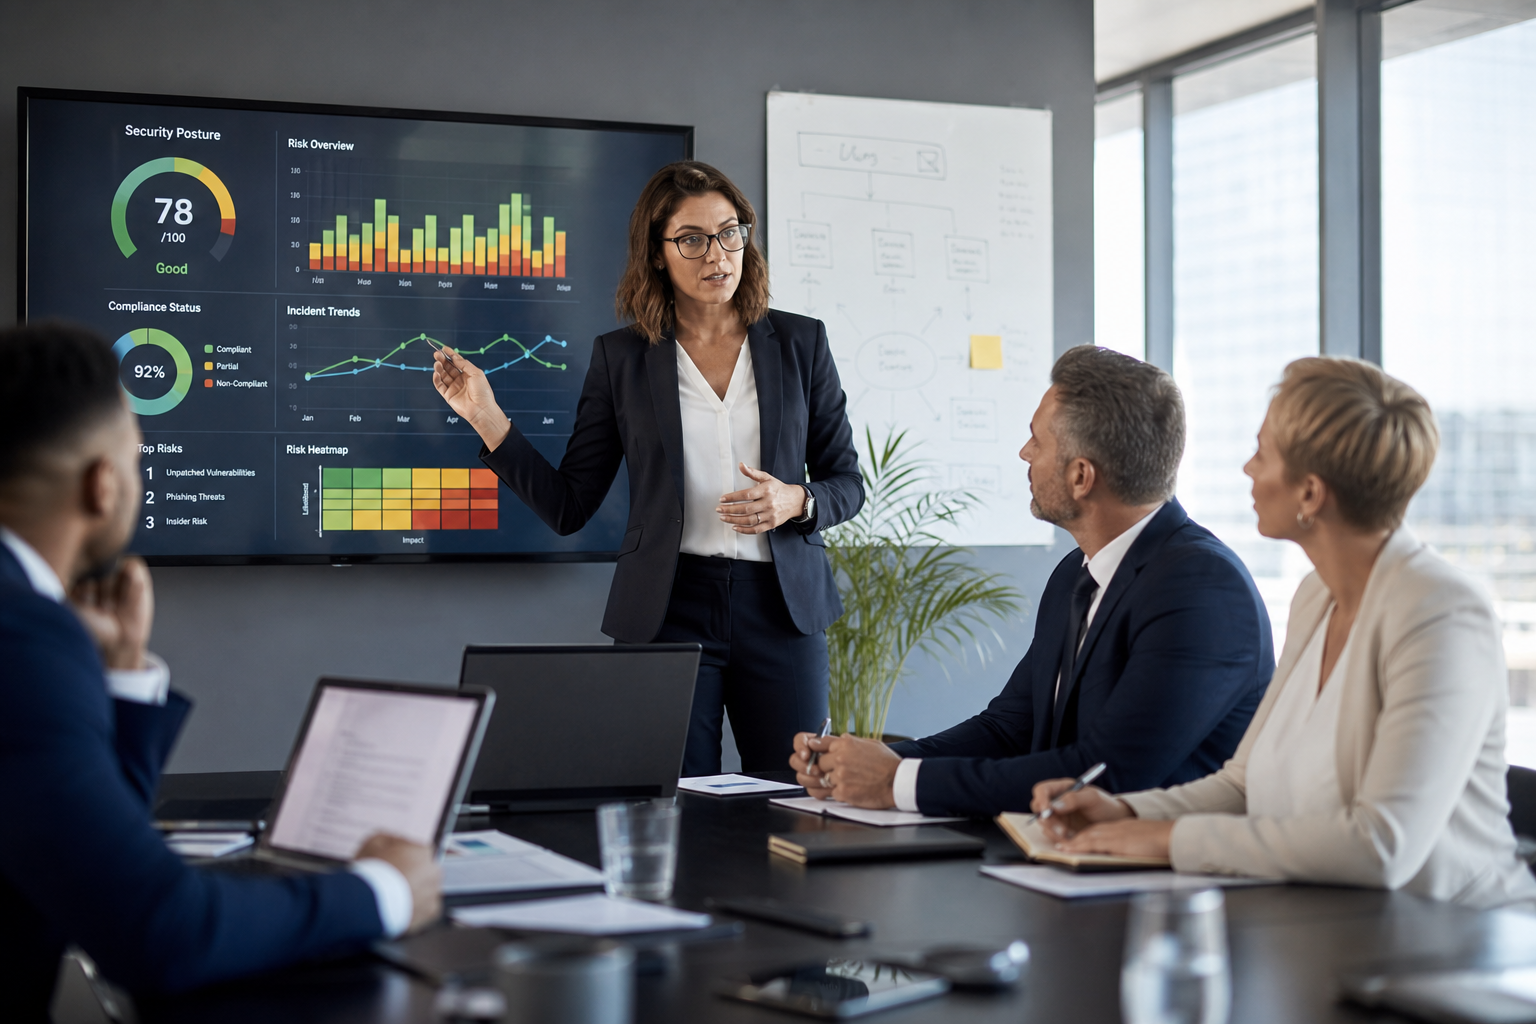
OXEN Penetration Testing helps organizations reduce uncertainty by validating whether existing cybersecurity investments provide effective protection against realistic threats. Leadership gains greater visibility into security exposure, potential business impact, and the improvements that should receive immediate attention. Prioritized recommendations support more efficient use of cybersecurity budgets, stronger compliance preparedness, and better-informed risk decisions. By identifying exploitable weaknesses before they contribute to an incident, organizations can strengthen resilience and protect operational continuity. Partnering with OXEN turns penetration testing findings into a practical strategy for measurable security improvement.
Ready to test your defenses?
Frequently Asked Questions
A vulnerability scan identifies known weaknesses using automated tools. A penetration test goes further: OXEN's team actively attempts to exploit those weaknesses (and others) to determine the real-world impact. Think of a scan as finding the unlocked doors and a pen test as actually walking through them.
OXEN tests external-facing systems, internal network environments, and optionally includes social engineering. Physical testing outside of onsite penetration tactics is not included in this offering.
Week 1 is dedicated to a kickoff meeting, information gathering, and provisioning the access and coordination your environment requires. You'll designate a single technical point of contact to work with OXEN throughout the engagement.
You receive a full technical report with an executive summary, detailed findings with technical evidence, impact analysis, and prioritized remediation steps. OXEN also delivers an executive briefing to walk through findings with your leadership team.
This is a project-based engagement. Pricing depends on scope (number of systems, external vs. internal, social engineering inclusion). Contact OXEN to discuss your environment and get a scoped estimate.
Physical security testing beyond onsite penetration tactics is out of scope. If you need physical security assessments (lock picking, tailgating, etc.), that requires separate scoping.
The report gives you a prioritized remediation list. OXEN can help you plan remediation through your existing managed services engagement, or discuss additional project work if needed. The pen test itself is an assessment, not a remediation service.
Annual testing is standard for most organizations, and is required by several compliance frameworks. Organizations that undergo significant infrastructure changes, add new systems, or operate in regulated industries may need to test more frequently.