Skip to content
OXEN_ITConsulting__1772727540815
Managed Continuous Threat Exposure Management (CTEM)

Stop Guessing.
Start Validating.

OXEN Managed CTEM provides continuous visibility into cyber risk by identifying, validating, and prioritizing exposures as technology environments evolve. Unlike point-in-time assessments, CTEM delivers ongoing discovery, testing, and risk analysis, helping leadership focus on the threats most likely to impact critical assets and business operations. The result is greater risk visibility, more effective security investments, improved resilience, and increased confidence in decision-making.
Circuit BG White

The OXEN Advantage

Organizations choose OXEN Technology because effective exposure management requires more than generating vulnerability data. It requires experienced professionals who can evaluate findings within the context of business priorities, validate whether exposures present a meaningful threat, and guide the organization toward practical improvements. OXEN combines continuous security validation, cybersecurity expertise, proactive management, strategic guidance, and executive-level reporting within one coordinated program. This approach helps organizations move beyond lengthy lists of technical findings and focus resources on the risks most likely to disrupt operations. OXEN simplifies exposure management while strengthening accountability, visibility, and measurable progress.
What’s Included

OXEN Managed CTEM combines continuous discovery, security testing, exposure validation, and risk-based prioritization into a structured, ongoing program. These capabilities help organizations understand their changing attack surface, distinguish meaningful risks from theoretical concerns, and direct improvement efforts toward the areas that matter most.

Continuous Exposure Assessment
Continuously identifies and evaluates vulnerabilities, misconfigurations, and security gaps across the environment.
Attack Surface Visibility
Provides ongoing visibility into internal and external assets that could increase organizational risk.
Penetration Testing & Validation
Validates exploitable vulnerabilities through controlled testing to determine real-world exposure and impact.
Risk-Based Prioritization
Focuses remediation efforts on the vulnerabilities and exposures that present the greatest business risk.
Remediation Guidance
Delivers actionable recommendations to help security and IT teams efficiently address identified risks.
Continuous Security Improvement
Supports an ongoing cycle of assessment, validation, remediation, and measurement to strengthen security posture over time.

Business Outcomes

OXEN Managed CTEM helps organizations reduce risk by directing attention and resources toward exposures with the greatest potential business impact. Continuous visibility improves decision-making, strengthens accountability, and enables security teams to address changing risks before they contribute to operational disruption. The program can also support compliance readiness by establishing a repeatable process for identifying, validating, prioritizing, and tracking security improvements. By partnering with OXEN, organizations gain a trusted advisor capable of transforming complex exposure data into a clear strategy for resilience, continuity, and long-term growth.

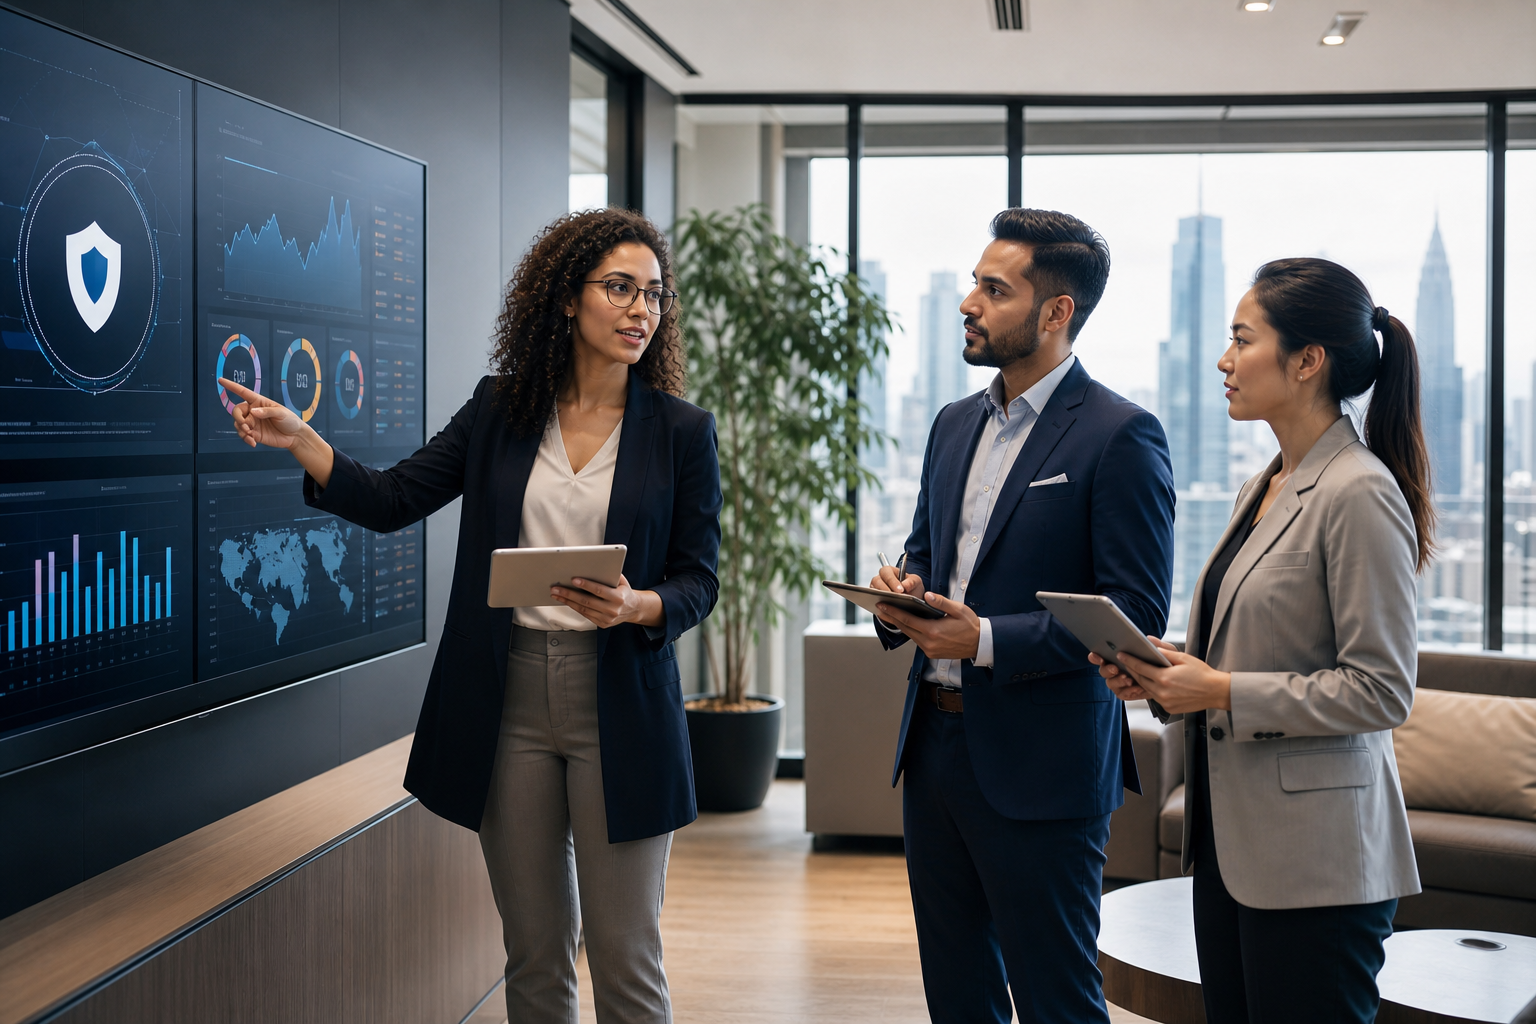
Cybersecurity Meeting With Digital Charts
Circuit BG

Ready to Close Your Security Gaps?

Frequently Asked Questions

What does CTEM stand for?

Continuous Threat Exposure Management. It's a managed service that delivers ongoing penetration testing and attack surface analysis throughout the year, rather than a single annual engagement. The goal is continuous reduction of your exploitable attack surface, not periodic snapshot reports.

How is CTEM different from a traditional pen test?

A traditional pen test is a one-time engagement that produces a point-in-time snapshot of your security posture. CTEM provides quarterly testing cycles that include remediation validation and new discovery each quarter. Your security posture improves iteratively rather than being reassessed once a year.

What does OXEN monitor vs. what are we responsible for?

OXEN conducts the attack simulations, maps the attack surface, prioritizes findings, delivers reports, and validates remediation through retesting. Your team is responsible for the actual remediation work, providing a technical point of contact throughout the engagement, and ensuring data backups are in place before testing begins.

How quickly does OXEN respond to a security incident discovered during testing?

If testing uncovers evidence of an active breach or critical exploitable vulnerability, OXEN communicates that immediately to your technical point of contact rather than waiting for the scheduled report delivery.

How is this different from vulnerability scanning?

Vulnerability scanning identifies known weaknesses by comparing systems against a database of vulnerabilities. CTEM goes further by simulating real attacks to validate which vulnerabilities are actually exploitable in your environment, and maps how an attacker would chain vulnerabilities together to reach critical assets. Scanning gives you a list. CTEM shows you the path.

What reports do we receive?

Each engagement delivers five reports: a technical assessment, an executive summary, a penetration findings report with technical details, a segmentation analysis showing how network segmentation performs against lateral movement, and a remediation roadmap with prioritized guidance.

Does CTEM include the actual remediation work?

No. OXEN provides detailed remediation guidance and validates fixes through retesting. Remediation is handled by your internal team or through a separate scoped project with OXEN.

Does this include physical security testing or manual penetration testing?

No. CTEM uses autonomous attacker emulation to deliver continuous, on-demand security validation. Physical security testing and manual penetration testing are not included in this service.