Why Patching Alone Doesn't Prove Security: The Missing Verification Step
Activity Does Not Always Equal Results
Many organizations measure cybersecurity success by the number of patches deployed or vulnerabilities addressed.
While these metrics are important, they do not always answer the most important question:
Has risk been reduced?
Effective cybersecurity programs focus on outcomes, not simply activities.
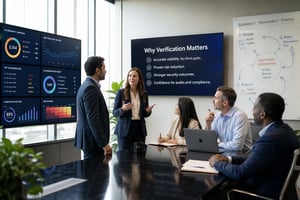
Why Verification Matters
Patches can fail.
Systems can be missed.
Configuration issues can prevent vulnerabilities from being fully remediated.
Without verification, organizations may assume risk has been reduced when exposure remains.
Verification provides confidence that remediation efforts have achieved their intended goal.
Executives Need Evidence of Progress
Leadership teams increasingly expect cybersecurity investments to produce measurable results.
Verification helps answer critical questions:
- Were vulnerabilities successfully addressed?
- Are security initiatives working?
- Is risk decreasing over time?
- Are investments generating value?
Organizations that can answer these questions gain greater confidence in their cybersecurity strategy.
Measuring Security Improvement
The strongest vulnerability management programs focus on:
- Identifying vulnerabilities
- Prioritizing risk
- Remediating findings
- Verifying outcomes
- Measuring progress
This structured approach creates accountability and supports continuous improvement.
How OXEN Helps
OXEN Vulnerability Management helps organizations validate remediation efforts through ongoing scanning, reporting, and visibility into security improvement initiatives.
This ensures leadership has confidence that risk reduction efforts are producing measurable results.
Confidence Comes From Verification
Cybersecurity strategies should not rely on assumptions.
They should rely on evidence.
Verify Progress and Demonstrate Results
The goal is not simply to deploy fixes. The goal is to reduce risk. Talk with an OXEN cybersecurity expert about how Vulnerability Management can help your organization validate remediation efforts and strengthen accountability.