When Cyber Insurance Doesn't Pay: The Costly Mistakes Organizations Make
Most business leaders assume cyber insurance exists to provide financial protection when the unexpected occurs.
While that is certainly true, another reality often receives less attention: not every claim is automatically approved.
Organizations across every industry have discovered that securing coverage and successfully collecting on coverage are two very different things.
As underwriting requirements become more rigorous, insurers are placing greater emphasis on cybersecurity controls, documentation, and organizational preparedness.
Understanding why claims are challenged or denied can help organizations strengthen both their cybersecurity programs and their position with insurers.
The Coverage Assumption
A common misconception is that cyber insurance functions like a guarantee against every cyber-related financial loss.
In reality, policies are contractual agreements that often contain requirements, obligations, exclusions, and conditions.
When organizations fail to meet expectations established during underwriting or policy administration, claim complications can arise.
This does not mean insurers are looking for reasons to deny claims.
Rather, insurers expect organizations to maintain the security controls and processes represented throughout the underwriting process.
Mistake #1: Controls Were Declared but Not Implemented
Insurance applications frequently ask whether specific safeguards are in place.
Examples include:
- MFA
- Endpoint protection
- Security awareness training
- Backup systems
- Incident response plans
Problems can develop when organizations indicate controls are present but implementation is incomplete or inconsistent.
Executives should work closely with IT and cybersecurity leadership to validate security claims before submitting insurance applications.
Mistake #2: Vulnerabilities Go Unaddressed
Organizations that routinely identify vulnerabilities but fail to address them create unnecessary risk.
Known vulnerabilities represent opportunities for attackers.
Insurers increasingly expect organizations to demonstrate ongoing risk management and remediation activities.
A documented process often matters just as much as the technology itself.
Mistake #3: Poor Documentation
Documentation remains one of the most overlooked components of cybersecurity governance.
Organizations may have strong controls but struggle to demonstrate them.
Important areas often include:
- Policies
- Security procedures
- Recovery plans
- Incident response plans
- Security training records
When documentation is missing or outdated, organizations may encounter challenges proving compliance with insurer expectations.
Mistake #4: Incident Response Weaknesses
The quality of an organization's response frequently influences the overall impact of a cyber event.
Without a documented and tested incident response process, organizations often experience:
- Delayed containment
- Extended downtime
- Higher recovery costs
- Communication challenges
Executives should ensure incident response capabilities are reviewed regularly and aligned with business continuity objectives.
Mistake #5: Insurance Applications Become Outdated
Cybersecurity environments evolve rapidly.
Organizations add systems, change vendors, implement new technologies, and alter business processes.
When insurance applications no longer reflect reality, risk increases.
Regular reviews help ensure underwriting information remains accurate and aligned with current operations.
Cyber Insurance Is a Partnership
The most successful organizations view cyber insurance as a partnership between risk transfer and risk management.
Insurance can play an important role in financial protection, but it works best when supported by strong cybersecurity practices.
Organizations that invest in preparedness often find themselves better positioned before, during, and after a cyber incident.
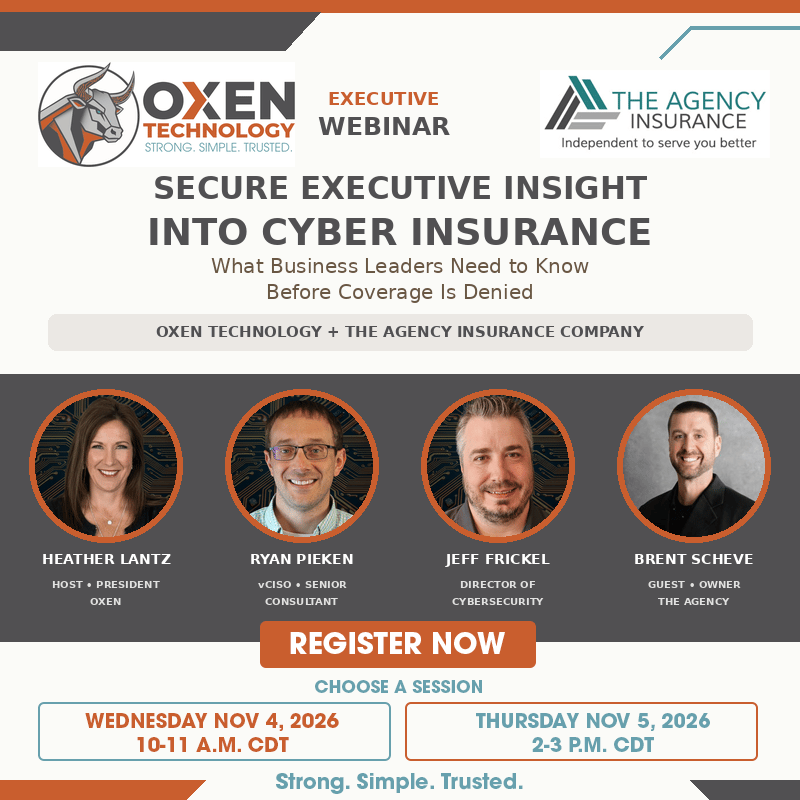
Join OXEN's Executive Webinar
Attend OXEN's upcoming webinar to learn how business leaders can strengthen insurability, improve cybersecurity maturity, and reduce the risk of costly claim complications.
Discover practical insights that help organizations align cyber insurance expectations with cybersecurity realities.